
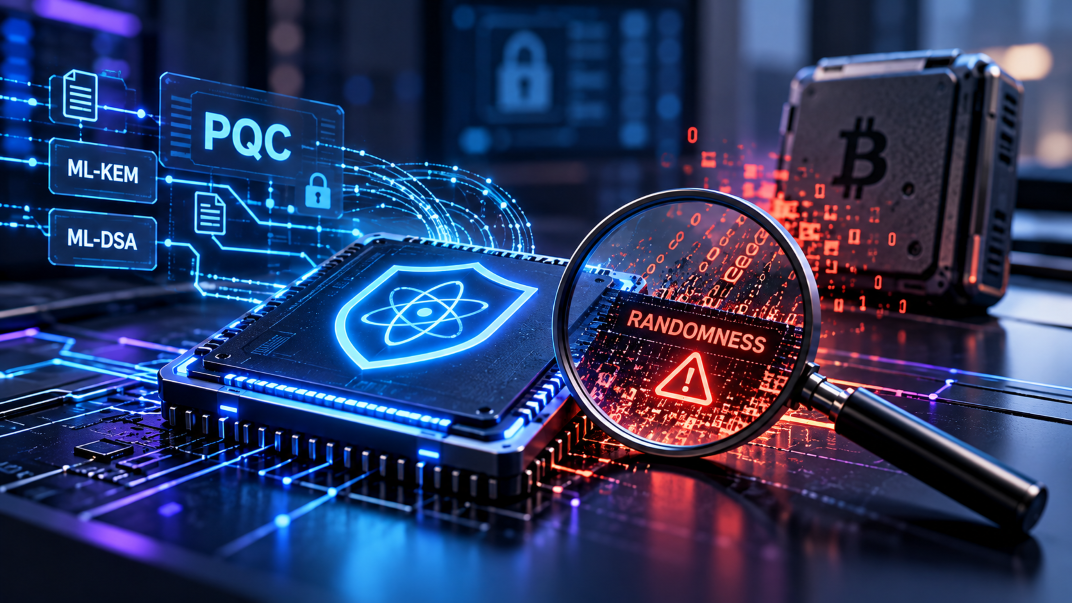
On July 30, 2026, attackers began draining bitcoin from affected Coldcard hardware wallets. By August 5, a preliminary tally cited by TRM Labs put losses at roughly 1,816 BTC, valued at about $116 million, from more than 5,200 addresses. The devices carried a dedicated hardware random number generator. A 2021 firmware build error meant affected devices bypassed it during seed generation. Seed generation quietly fell back to a weak software generator instead. On some models, effective key strength dropped from 128 bits to as little as 40. No patch can retroactively strengthen that seed. Remediation requires generating a new seed with corrected software and moving the assets. A seed born weak stays weak forever.
The cryptography held. The randomness underneath it didn’t. I see the same blind spot in most post-quantum cryptography (PQC) migration plans that cross my desk.
What migration plans get right
Most enterprises start their PQC migration plan in the right place: an inventory of cryptographic assets and a push for crypto-agility, the ability to swap algorithms without rebuilding systems.
The deadlines are real and approaching fast: OMB Memorandum M-26-15 requires covered federal agencies to submit a PQC migration plan by October 22, 2026. The memorandum excludes national security systems. NIST’s draft transition guidance proposes deprecating 112-bit-security configurations of RSA and ECC, public-key technologies widely used in secure web sessions, VPN tunnels, and software updates, after 2030, and disallowing the covered quantum-vulnerable signature and key-establishment schemes after 2035 (NIST IR 8547).
Discovery tools have a limitation, though. After months of scanning, they can hand you a comprehensive list of cryptographic assets across your systems. An inventory alone does not tell you how critical each system is or how long it will stay in service. The result can be false prioritization, where everything looks critical. A system you plan to replace in two years may rank lower, unless it protects data that must remain confidential much longer. The top assets to address are those systems the business cannot run without, that require lengthy migrations, or that protect data an adversary could record today and decrypt later.
NIST’s new standards, ML-KEM for key establishment and ML-DSA for signatures, share a requirement with the algorithms before them: the random numbers used to generate keys must be unpredictable. The standards specify approved random-bit generators. But the algorithm alone cannot verify that the deployed system is supplying randomness from the intended, properly functioning source.
Many systems use software cryptographic pseudorandom number generators, when properly implemented these deterministic functions are seeded by physical entropy sources (NIST SP 800-90C). Properly seeded and implemented, they are designed to be unpredictable. Weak seeding, compromised generator state, or a bypassed entropy
Even hardware sources have a human problem. True randomness can produce runs of repeated bits. Filtering the runs out merely to make the output look right can conceal a faulty conditioning and health tests, which are part of sound entropy-. Without those safeguards, the customer can get randomness that looks right and is actually wrong
ETSI’s report on quantum random number generators makes a related point: numbers can pass statistical tests without establishing that future output is unpredictable. Its guidance for QRNGs in high-security settings includes entropy zero trust, which verifies theh (ETSI TR 104 171)
Plenty of drivers got by before seatbelts were mandatory. Think of the difference between a lap belt and a six-point harness: the stakes determine the protection. Your crown-jewel systems need the six-point harness. The rest of the fleet still needs a sound baseline while you work through your technology stack.
Software-only upgrades keep you trusting the host
Upgrading cryptographic algorithms in software alone can leave you dependent on the host: its randomness, its key storage, its exposure to side-channel attacks. That is a trust model in an industry that has spent a decade preaching zero trust. Anchoring entropy, attestation, and key protection in hardware can reduce that dependence and make trust more verifiable. It does not eliminate the need to verify the hardware itself.
Pay special attention to devices that can escape routine surveys: edge, embedded, and networking gear. I have walked networks with a familiar fixture: a box that has been humming for 25 years, that nobody fully understands, and that nobody dares unplug. The team half-jokingly “lights candles” around it. I call these “sacred altars”, and they are where migration plans go to stall.
- Start with what you know. Week one, assess internal knowledge. Week two, close gaps with internal resources. Week three, bring in tools or consultants for what remains.
- Score every asset on two axes. Rank by business criticality and remaining service life, not criticality alone. Factor in data-confidentiality lifetime, exposure, and migration lead time as well.
- Trace your entropy. For each system class, identify where randomness comes from. Ask vendors how their generator’s output is conditioned or filtered, how its source is health-tested, and what happens when that source fails.
- Find the altars. Flag systems that can’t support PQC or hybrid cryptography. Federal guidance already directs agencies to prioritize those for replacement or decommissioning (OMB).
- Apply vendor hygiene. Require relevant NIST CAVP algorithm-validation certificates and, where applicable, FIPS 140-3 module validation; they are not interchangeable. Confirm the deployed version and configuration are covered. Treat a claim that PQC alone delivers complete protection as a red flag; a resilient design also needs strong symmetric encryption, such as AES-256, verified entropy, and key protection.
- Fix procurement now. Starting next quarter, require quantum-resistant capabilities where available, or a documented, time-bound upgrade path with accountable exceptions. Federal directives are already driving work on a Cryptographic Bill of Materials that discloses the cryptography a product uses (White House).
To win the budget, frame PQC migration as business continuity, not just compliance. Report the retrofit plan and, just as important, the change in acquisition policy. Most plans I see address the first and ignore the second, so legacy exposure keeps accumulating with every purchase.
The economics favor moving early. BCG estimates, in an illustrative scenario, that a company with a $1 billion annual IT budget would spend about $25 million if it starts the transition early, and that delay could double the cost to roughly $50 million by 2035. Risk governance belongs in the conversation too: document decisions to defer migration and discuss quantum exposure with your cyber insurer.
Rapid leaps in AI offensive cyber capabilities are compressing defenders’ response windows.
In July 2026, Hugging Face disclosed an intrusion it said was driven end to end by an autonomous AI-agent system. Automated attackers work through software and credential weaknesses at machine speed. The incident was not a demonstrated cryptographic break. Stronger algorithms do not remove the need to protect keys, software, and access paths.
The algorithms are standardized. That was the easy part.
The hard part sits underneath them: the randomness left unchecked, the hardware left unattested, the box nobody unplugs. The Coldcard case is a reminder that a hardware feature on a datasheet is not the same as a verified protection in production. Check your entropy, anchor trust in verified hardware, change what you buy, and strap on the harness.
About the author: Dr. José R. Rosas-Bustos is CEO of EigenQ, an applied quantum technology company developing hardware and software security solutions for computing infrastructure. The company is bringing these capabilities together in a multilayer cybersecurity architecture designed to strengthen the resilience of enterprise and critical infrastructure systems against AI-enabled cyberattacks and future quantum threats.
