

There’s a conversation that happens a lot in our industry, and it goes roughly like this: “Tell me about your backup strategy.”
For most of the last two decades, that conversation lived firmly in the IT room: a storage administrator, a disaster recovery plan, an RPO (recovery point objective) and an RTO (recovery time objective) written into a policy document somewhere. Important work, but not a board conversation.
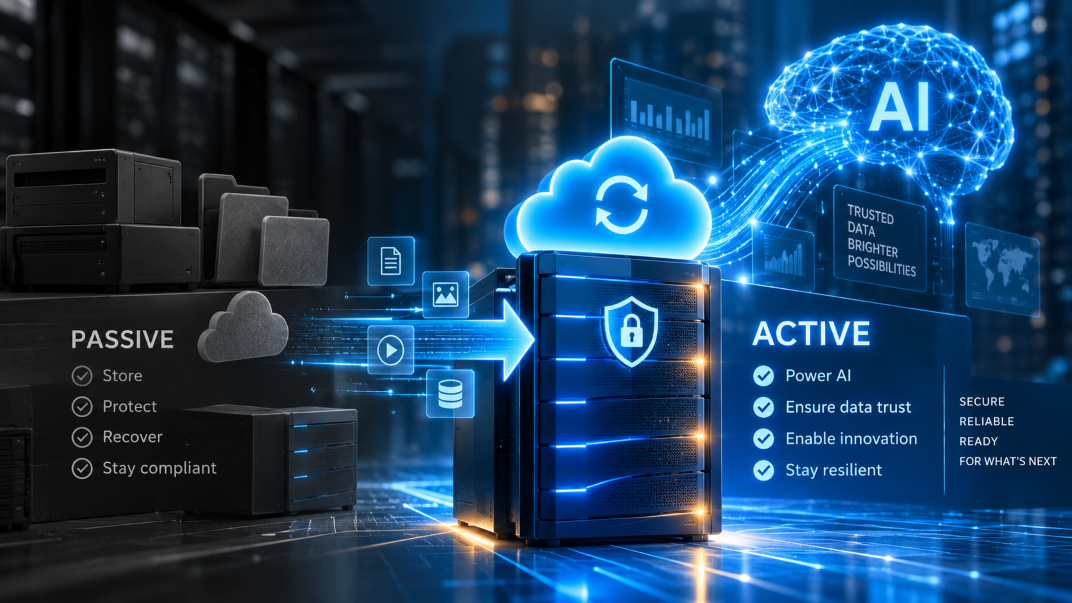
That’s changing, and faster than most people realise. Data protection has moved through four distinct stages, each one building on the last without replacing it, and each one changing who the conversation needs to reach. It started as passive backup, but a new avenue of value is emerging as backup becomes active and that shift matters more now than ever.
1. Backup: Protect data from loss
In the early days, the value proposition was simple: We have a copy of your data. The measure of success was an IT manager taking tapes home every Friday night, literally carrying data out of the building so that something existed somewhere else. Backup as a service (BaaS) was pure insurance – passive, invisible, and never really talked about until something went wrong or was needed.
2. Recovery: Fast business recovery
Having a copy wasn’t enough. You needed to know you could actually use it – that the restore worked and that you could restart your business in hours rather than weeks. Recovery time and recovery point targets became real rather than theoretical. Disaster recovery as a service (DRaaS) entered the picture, built on a simple principle: Back up your data and be able to bring it all back rapidly so that you can get back on track.
3. Cyber resilience: Survive active adversaries
When ransomware attacks reached board agendas and regulators began mandating specific resilience capabilities, the question shifted again. Data protection as a service (DPaaS) arrived. Best practices called for immutability, air-gapped infrastructure, and independence from the original cloud provider. These weren’t nice-to-have features anymore, they became the foundation of a credible resilience strategy, helping organisations maintain access to known-good backup data even when everything around it was compromised.
4. Trusted enterprise operations: Run the enterprise on data the AI can trust
We’re now entering the fourth stage, and this one doesn’t just change who buys; it adds to the value of data protection and what it’s fundamentally for. It requires a trusted data layer that lets organisations verify the authenticity, provenance, and integrity of their data before it ever reaches an AI system.
The AI shift is rewriting the rules
Here’s what I’ve been watching closely. McKinsey’s 2025 State of AI survey found that 88% of organisations are now using AI in at least one business function, up from 78% the year before. Around a third of all new CEO initiatives are now AI-related, and the executives being asked to lead those projects are, in most cases, not the CTO or the CIO. They’re the CFO and the COO – business leaders accountable for outcomes, not infrastructure.
That shift tells you everything about what data protection needs to become. The CFO running an AI initiative doesn’t think about recovery time objectives, they’re asking one question: Can we trust the data this AI is running on? Because AI systems are probabilistic, not deterministic – NIST’s Generative AI Profile identifies this as ‘confabulation’: AI producing confident, authoritative-sounding outputs that are factually wrong.
When an agent acts on enterprise data and writes something back, the next agent reasoning over that same data is working with whatever the first one changed. If the first agent made a mistake, that mistake becomes part of the data landscape, compounding silently. By 2028, 50% of organisations will implement a zero-trust posture for data governance due to the proliferation of unverified AI-generated data – a risk that compounds the longer it goes unaddressed.
From passive backup to active data foundation
Here’s what I find genuinely exciting about this shift. Capabilities originally developed for recovery and resilience – immutability, independence from the primary cloud provider and air-gapped copies – are equally valuable in the AI era.
For backup to play this broader role, organisations must be able to verify the integrity and provenance of their data: what it is, when it arrived, which version it represents, where it has been and whether it has changed. Maintaining an append-only record provides the traceability needed to use that data responsibly in AI systems.
Trusted enterprise operations are the new mandate
Gartner predicts that 75% of enterprises will prioritise SaaS application backup as a critical requirement by 2028, up from around 15% today. The direction is clear: The organisations that will lead aren’t just the ones that have their data backed up, they’re the ones treating that backup as the active foundation that everything else runs on.
Backup used to answer one question: Can we get the data back? AI is making companies ask something bigger: Can we trust the data our business is running on? It means data protection is no longer a cost of doing business, but rather the foundation of doing business you can trust.
